
News
CMMC news, in plain words.
What changed in CMMC and what it means for a small contractor, checked against the official sources.
Cybersecurity Awareness Month 2026: CISA’s four habits line up with CMMC
CISA opened Cybersecurity Awareness Month on 1 October 2026 with four basic habits. Each one lines up with a CMMC Level 2 requirement for defense contractors.
Help for small defense contractors, much of it free, and what it cannot do
APEX Accelerators, NIST and CISA each offer help for small companies, much of it at no cost. Here is what each one does, and what it cannot do for you.
FedRAMP Moderate is now called Class C. Your contract still says Moderate.
FedRAMP has renamed its cloud baselines. Class C now covers the old Moderate baseline, the one your contract asks of a cloud service that holds your CUI.
Revision 3 of NIST SP 800-171 is out, but defense work still uses Revision 2
NIST published Revision 3 in May 2024. Defense contracts and CMMC Level 2 still use Revision 2. A proposal for all federal contracts names Revision 3, but it is not final.
A proposed rule would set the same CUI rules for all federal contracts
A June 2026 proposal would set one clause, one form and NIST SP 800-171 Revision 3 for sensitive information in federal contracts. It is not final and can change.
New numbers for the cybersecurity clauses in your contracts
The federal and defense contract rules have been rewritten, and some cybersecurity clauses got new numbers. The security work behind them has not changed.
Three cyber settlements, one lesson: your score must be true
Between December 2025 and September 2026, three companies doing defense work agreed to pay to settle claims that they lacked the cybersecurity their contracts required. One is a machine shop.
The government can still check your cybersecurity score
The pause of outside CMMC assessments does not stop government assessors from checking your NIST SP 800-171 work. A result from the Defense Contract Management Agency outranks your own score.
You can still get a CMMC Level 2 certificate from an outside assessor
The Cyber AB says outside certification assessments for CMMC Level 2 go on despite the pause. A certificate also meets a self-assessment requirement for the same systems.
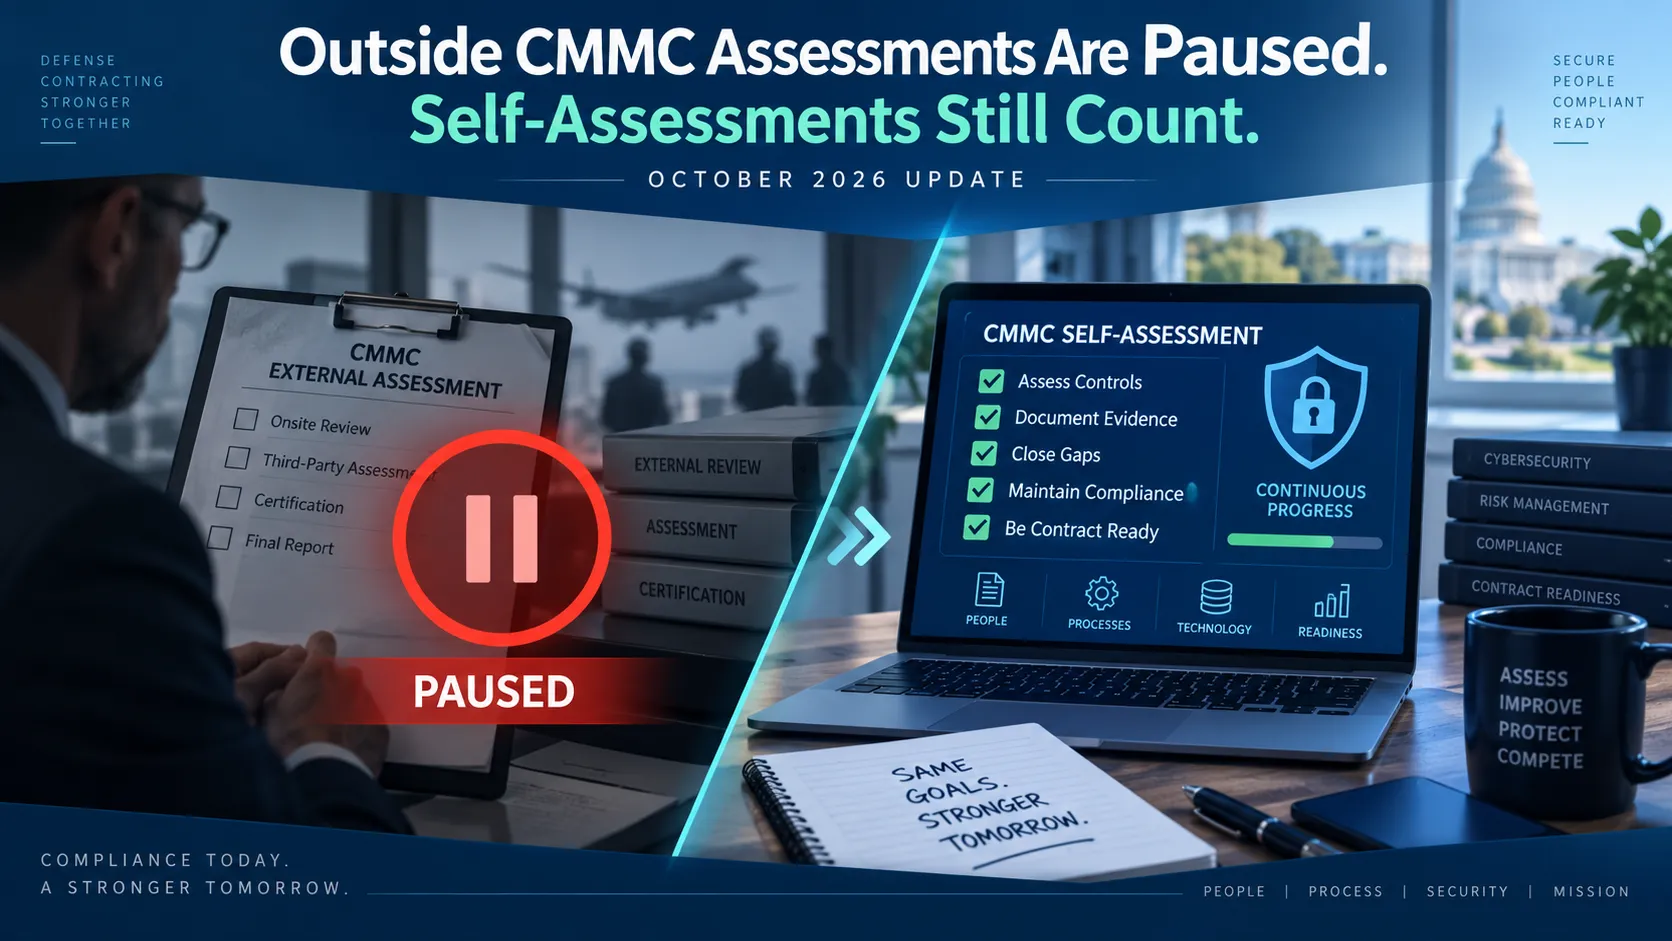
Outside CMMC assessments are paused. Self-assessments still count.
The Department of War has paused the step that would have required an outside assessment for many contracts from November 2026. Your self-assessment, your SPRS entry and your yearly confirmation all still apply.
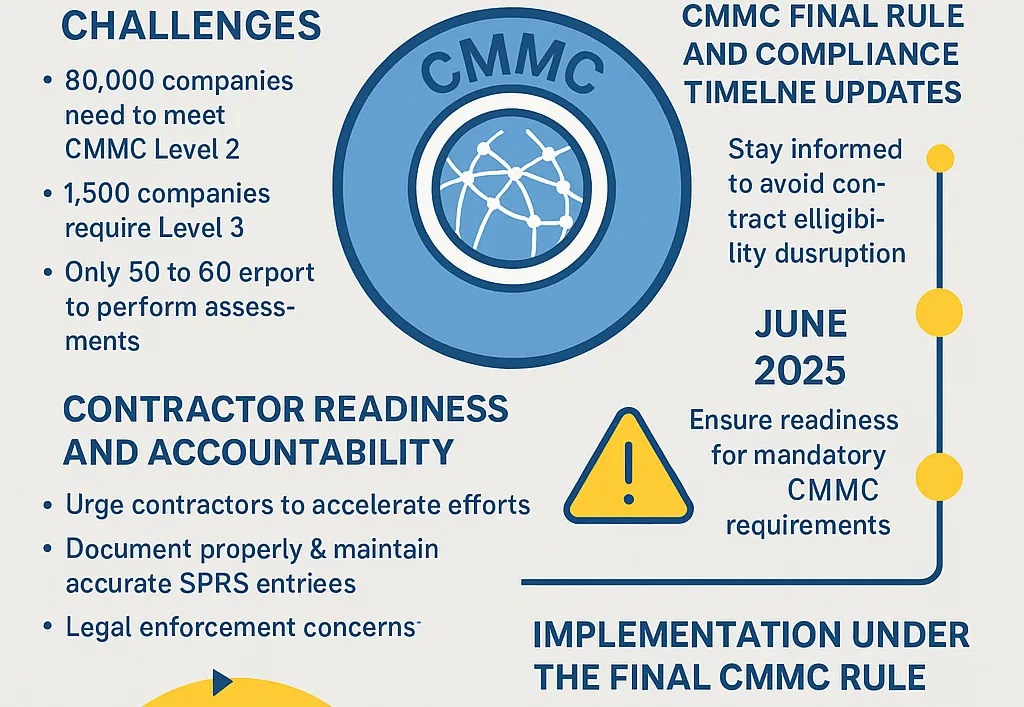
CMMC June 2025 Update
DoD Addresses Challenges to Make CMMC a Reality: CMMC June 2025 Update Introduction As the Department of Defense (DoD) continues the phased [...]
May 2025 CMMC Compliance Update: Legal Action, False Claims, and What Contractors Must Know Now
May 2025 CMMC Compliance Update As the Cybersecurity Maturity Model Certification (CMMC) 2.0 framework moves from policy to legal mandate, May [...]
Learn more
Earlier articles
CMMC June 2025 Update
DoD Addresses Challenges to Make CMMC a Reality: CMMC June 2025 Update Introduction As the Department of Defense (DoD) continues the phased [...]
CMMC Level 3
CMMC Level 3 The Cybersecurity Maturity Model Certification (CMMC) has emerged as a crucial framework for organizations working with the [...]
CMMC Level 2
CMMC Level 2 The Cybersecurity Maturity Model Certification (CMMC) is a vital framework designed to enhance the security posture of contractors working [...]
CMMC Level 1
What is CMMC Level 1? In today's digital world, cybersecurity is more important than ever, especially for businesses that deal with sensitive [...]
What is CMMC?
Discover the Cybersecurity Maturity Model Certification (CMMC), a crucial framework for enhancing cybersecurity in organizations working with the Department of Defense.
Get ready for CMMC with your own site.
A short call, using a sample company. No obligation.